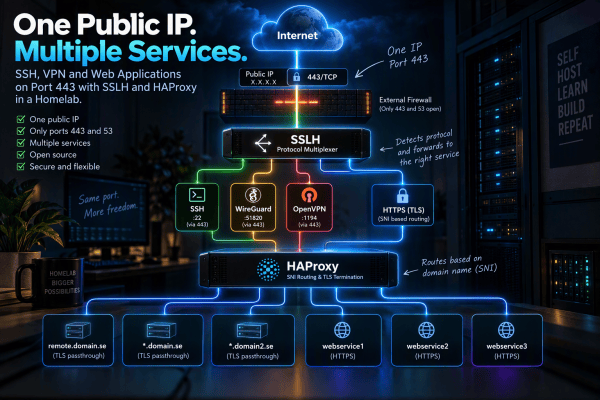
Problem to solve I have many webservices and vpn and other service that I want to be able to access from Internet in my homelab. But the issue here is that I only have one external ip. And I want to with opensource applications. The only thing that is not Opensource is external firewall. I... Continue Reading →
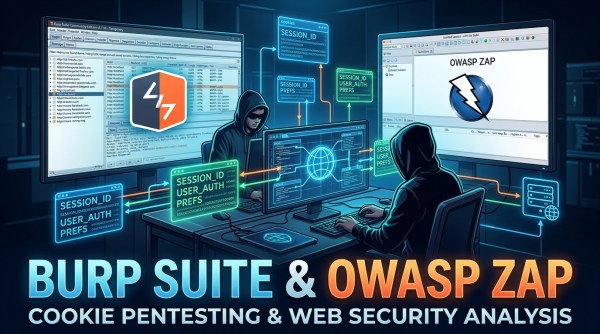
Automating dynamic session cookie handling in OWASP ZAP and Burp Suite during application penetration testing.
Why I created a Dynamic Session Cookie Script for OWASP ZAP and script for BurpSuite Community Edition When performing security testing with OWASP ZAP or Burp Suite especially when using features such as Resend, Fuzzing or repeated API requests session management can become a challenge. Some applications regularly refresh or rotate their session cookies. In... Continue Reading →